News
Expanding Globally? What Should Life Sciences Companies Really Know About Data Privacy?
Introduction
Global expansion is one of the most ambitious moves a Life Sciences company can make. New markets mean new patients, new partners, and new growth opportunities. But they also mean new rules, and when it comes to Data Privacy, those rules vary far more than many business leaders anticipate. GDPR compliance is a solid foundation, but on its own, it will not carry you once you operate beyond European borders. Going global calls for a broader, risk-based approach to Data Privacy, and increasingly, a strategic one.
GDPR Is a Strong Foundation, But Not a Global Passport
There is no question that the General Data Protection Regulation set a global benchmark. Its influence can be felt in legislation across dozens of countries, and being GDPR-compliant signals a serious commitment to Data Protection. For Life Sciences companies headquartered or operating in Europe, it is an essential baseline.
But baseline is the operative word. GDPR does not travel with you. The moment your clinical trial extends to a site in Japan, or your commercial operations reach patients in California, you enter a different regulatory environment, one with its own definitions, obligations, and enforcement mechanisms. Treating GDPR as a universal compliance solution is not just legally insufficient; it is a strategic blind spot.
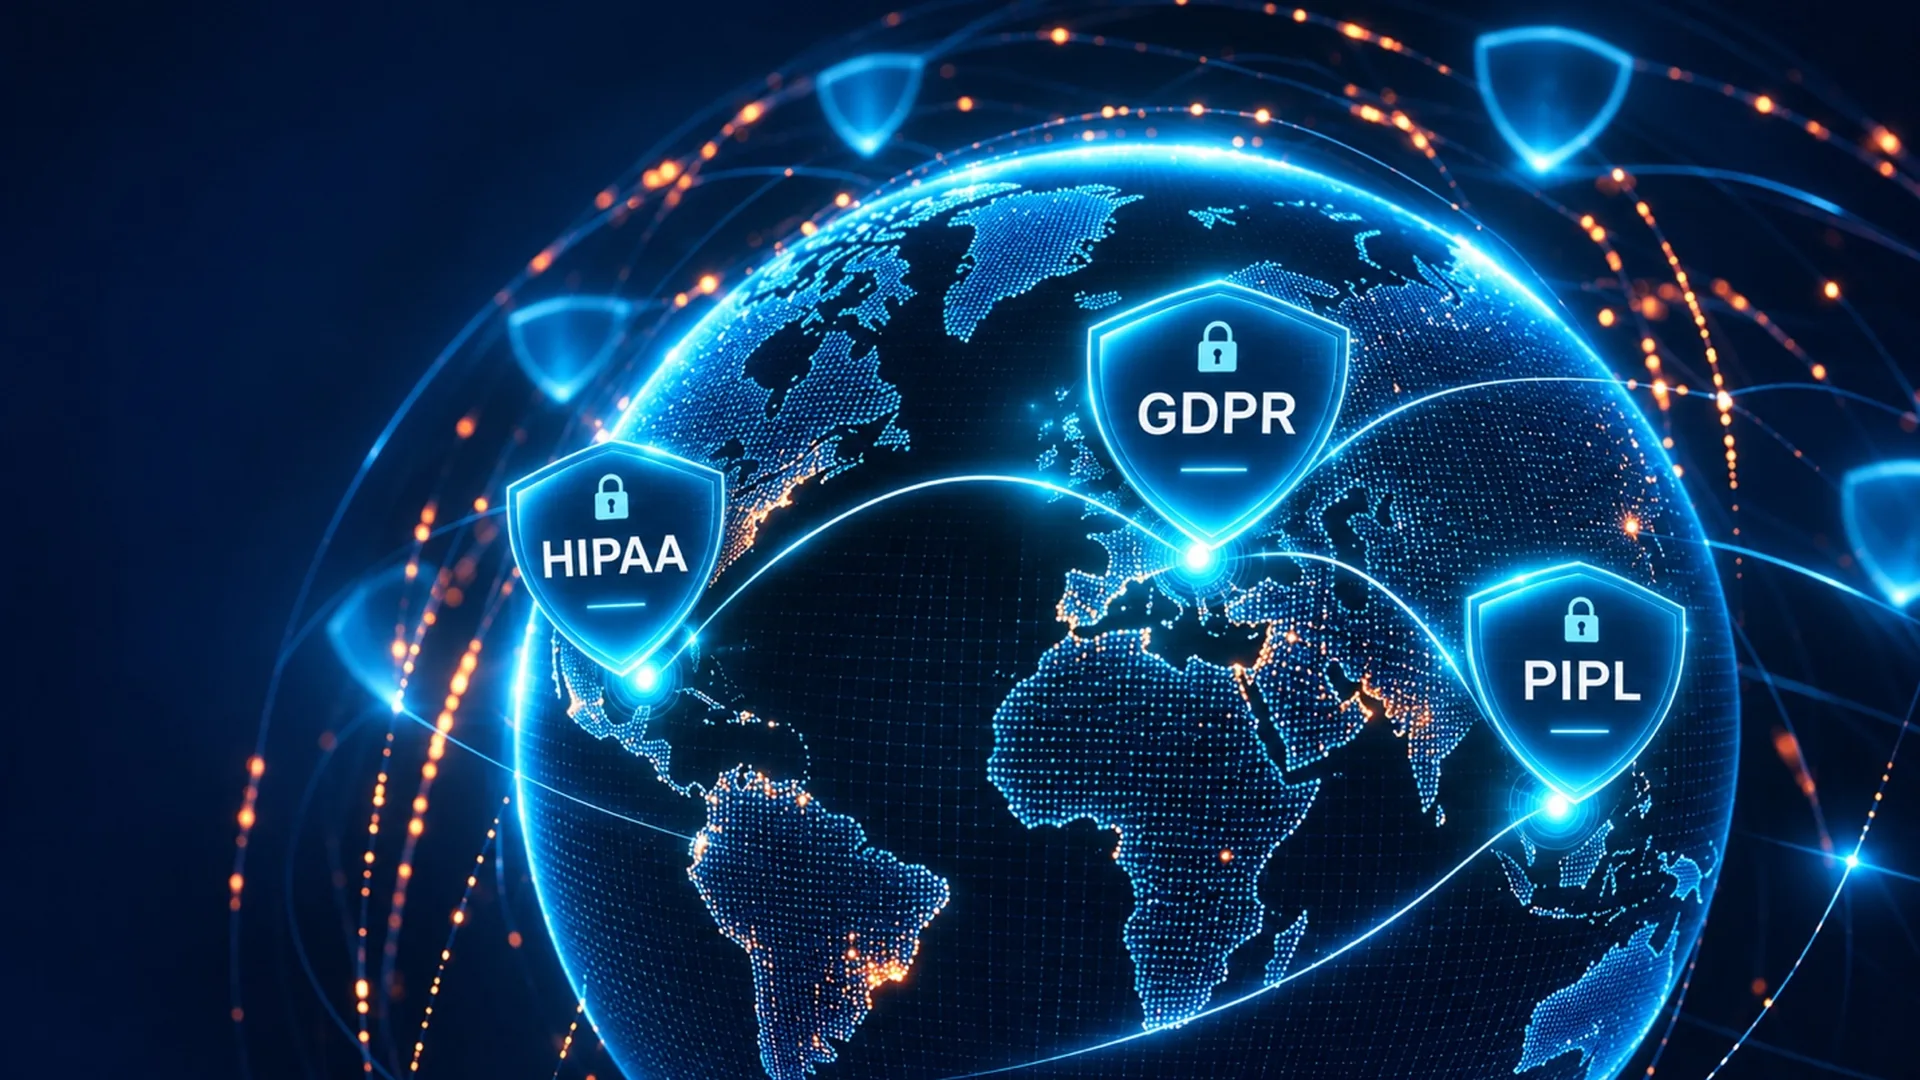
In practice, three broad families of regimes emerge, each calling for a different approach. First, GDPR-like frameworks, such as Brazil’s LGPD or South Africa’s POPIA, where familiar concepts apply but local registration, representation, and notification duties still differ. Second, regimes that layer strong local requirements on top, typically involving international transfers, mandatory contractual language, or imposed consent templates. Third, jurisdictions built on a different logic altogether sectoral and sub-federal rather than omnibus with the United States being the clearest example. The difficulty is rarely a single law; it is moving between the three.
The United States: A Patchwork That Demands Attention
The United States has no single federal Data Privacy law equivalent to GDPR. Instead, Life Sciences companies must navigate a layered system of federal sector-specific regulations and rapidly evolving state laws.
HIPAA remains the cornerstone for health data in the US, governing how protected health information is collected, used, and disclosed by covered entities and their business associates. For Life Sciences companies conducting clinical research or partnering with healthcare providers, HIPAA compliance is non-negotiable. However, HIPAA does not cover all health-related data, a gap that becomes increasingly significant as companies collect data through digital health tools, wearables, or patient-facing apps.
At the state level, California’s Consumer Privacy Act (CCPA), as amended by the CPRA, has introduced GDPR-adjacent rights for California residents, with more states following suit. For any company with a US commercial presence, this fragmentation rules out a one-size-fits-all strategy.
Japan and APAC: A Region in Regulatory Motion
The Asia-Pacific region presents a dynamic and increasingly demanding Data Privacy landscape. Japan’s Act on the Protection of Personal Information (APPI) has undergone significant reforms in recent years, moving closer to GDPR standards while retaining distinct local requirements. For Life Sciences companies operating clinical trials or managing patient data in Japan, understanding APPI’s specific rules around sensitive data, third-party provision, and cross-border transfers is critical.
Beyond Japan, the broader APAC region offers no single regulatory framework. South Korea’s PIPA, Singapore’s PDPA, and China’s PIPL each come with their own obligations, and China’s regime introduces some of the most stringent data localization and transfer restrictions in the world.
Clinical Research: Where the Stakes Are Highest
In the context of clinical research, the implications of getting Data Privacy wrong are especially serious. Multinational trials involve the transfer of sensitive health data across multiple jurisdictions simultaneously. Sponsors, contract research organizations, and site networks must align on which legal frameworks apply, how data transfer mechanisms are structured, and what patient consent obligations exist in each country.
A consent form valid under GDPR may not satisfy APPI requirements in Japan, and in a number of countries, the local template is effectively imposed, leaving little room for a single global document. A data transfer mechanism compliant with US standards may not meet China’s PIPL obligations. These are not theoretical edge cases; they are practical challenges that can delay trial timelines, trigger regulatory scrutiny, or compromise data integrity.
Building Data Privacy compliance into the design of multinational studies from day one, rather than retrofitting it at the end, is the approach that separates organizations that scale efficiently from those that encounter costly setbacks.
What Business Leaders Should Take Away
For C-suite executives leading global expansion, the message is clear: Data Privacy is not a compliance checkbox to be delegated entirely to legal or IT teams. It is a strategic enabler or, if mismanaged, a strategic risk.
Three practical priorities stand out. First, map your data flows before you enter a new market. Understanding what personal data you collect, where it goes, and who accesses it is the foundation of any compliant international operation. Second, engage local expertise early. Regulatory nuance matters, and what works in Brussels may not work in Tokyo or San Francisco. Third, build a compliance architecture that is modular and adaptable, one that can accommodate new jurisdictions without a complete rebuild with every expansion and that prioritizes effort based on real risk rather than a checklist.
Conclusion
Global expansion in Life Sciences is an exciting opportunity and a genuine regulatory challenge. The companies that succeed are those that treat Data Privacy not as a barrier to growth, but as a discipline that, when properly embedded, enables it. GDPR is where the journey starts, not where it ends.
MyData-TRUST supports Life Sciences companies at every stage of their international development, providing the regulatory expertise and hands-on guidance needed to navigate complex, multi-jurisdictional Data Privacy requirements with confidence. Wherever your expansion takes you, we can help you get there, compliantly.
Authors: Victoria Derumier & Emeraude Camberlin